
When your best feature becomes your most expensive bug
A real experience from July 22, 2026: how one everyday feature of the POJISTENI.cz website turned into its most expensive bug overnight, and how quickly the fix was found.
It was an ordinary day. Then came something nobody expected.
František Sýkora is calmly having his morning coffee. Nothing suggests today will be any different from all the others.
Then a colleague from IT calls him. The numbers they track every day suddenly don't add up. Something is eating the company's money. And nobody yet knows what.
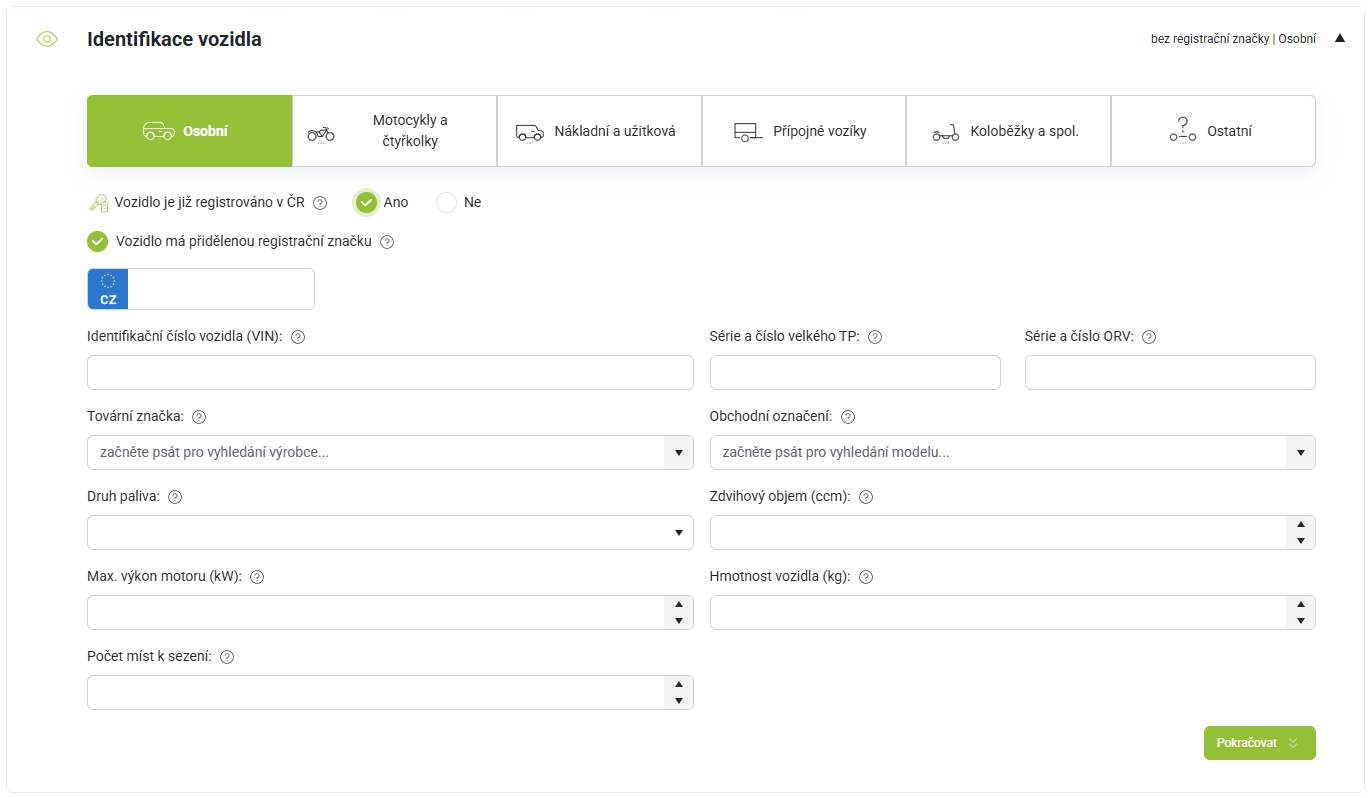
Behind it all is one everyday feature of the POJISTENI.cz website that nobody thought was a risk: you enter a license plate and the form fills itself in. Make, model, engine size, year. A few seconds instead of copying from the vehicle registration certificate, and the mandatory liability insurance price appears. Second nature.
Behind that convenience, though, is an operational reality the customer never sees: every single query costs something. The data is pulled from a paid registry, and every individual license-plate lookup is billed. At hundreds to thousands of requests a day, that's a predictable cost in the thousands of crowns. A model that makes perfect sense.
For exactly as long as every query comes from a real customer.
This wasn't a bug in the code
Here's the uncomfortable part that makes this worth reading to the end: nothing was broken. No unpatched vulnerability, no outdated version, no developer mistake. The feature did exactly what it was built to do.
An attacker simply started using it in an automated way. They deployed bots that generated license-plate queries at scale. Not hundreds a day. Thousands a minute. The peak amounted to roughly a thousand times normal traffic.
Costs didn't rise. They spiked.
The trap: both options are a loss
When this happens, you're facing a choice with no good answer.
And pay hundreds of thousands a day for queries that will never turn into a single policy.
And stop paying, but the customer who came to get a quote hits a wall. They leave for a competitor, and with them goes the line „it doesn't work".
POJISTENI.cz had to restrict the feature. Customers went back to copying details from the registration certificate by hand instead of three seconds. The bleeding stopped, but the wound stayed open.
This is the moment that decides everything. Not whether you stop the attack, but how long you keep paying in both directions — in money and in customers.
From the first signal to full recovery, in a matter of hours
Traffic monitoring revealed a sharp, unusual spike in queries to the license-plate auto-fill feature.
The „Under attack" mode made it possible to go straight to where the affected website belongs and trigger activation of WEDOS Protection.
After registration, the affected domain was placed behind a protective layer that evaluates every incoming request.
By changing the DNS, all traffic began routing through WEDOS Protection first. Real visitors carry on unaffected. Automated queries are stopped.
A protection level matching the nature of the attack was selected.
Once protection confirmed traffic was under control, data lookups resumed. The calculator was back for customers, fast and unrestricted.
Traffic is visible in a dashboard around the clock, so it's immediately clear what protection is catching and what value it delivers.
Custom error and verification pages styled to POJISTENI.cz's own brand design, so the protective layer feels like a natural part of the website.
No application changes. No rewriting the form.
A DNS change and a decision about who gets through.
Traffic keeps running. The bots don't.
Malicious queries are caught before they can trigger a paid lookup in the registry.
Direct spending on queries returned to its usual daily level.
Real customers can once again get a liability-insurance quote without any restrictions.
No more feature outages means no more negative reviews.
„This is definitely an experience worth sharing. POJISTENI.cz recommends WEDOS Protection, which solved more than just this one issue."
Why this affects you too
It's easy to read this case as „an insurance portal's problem". It isn't an insurance portal's problem. It's the problem of every company that offers customers a useful feature where every single use costs something.
Try finding anything from this list on your own website:
- → Looking up a company by registration number in a registry
- → Verifying a phone number by SMS
- → A form submission that triggers an email or notification
- → Generating a PDF, quote, or calculation
- → A connection to any paid API: exchange rates, geocoding, pickup points, shipping
- → Full-text search over a large database
- → Any endpoint with an AI model behind it
If you found at least one item and don't have a layer in front of it that distinguishes a customer from a bot, you have exactly the same exposure POJISTENI.cz had before the attack.
And the economics are against you. The attacker pays practically nothing for their query. You pay for every single one. With the rise of AI, the effort needed to prepare such an attack has dropped to almost nothing: a bot can be assembled in minutes, scaled to thousands of requests per second, and aimed precisely at the one feature that costs you money with every use.
The target is no longer „big infrastructure". The target is the single most useful thing you offer your customers.
Speed
Today, an attack can be prepared with AI in minutes and launched at thousands of requests per second.
Target
The target isn't infrastructure, but a specific useful feature that costs the company money with every use.
Standard
Continuous traffic protection is becoming an operational given, not a premium extra.
Protect what brings your customers to you
POJISTENI.cz resolved this situation in a matter of hours, because they noticed in time and deploying WEDOS Protection meant a DNS change, not rewriting the application.
Get a free assessment of where an attack could target your websites and applications, and how WEDOS Protection can prevent it.